
The EU AI Act's August Deadline Arrives — Just Not the One Everyone Expected
Insight . Intelligence . Accountability
A new wave of professionals is transforming Governance, Risk, and Compliance from a rigid framework into a dynamic force for trust, innovation, and resilience. Governance, Risk, and Compliance (GRC) has long been associated with boardrooms and bureaucracy—a domain reserved for executives and auditors. But that image is changing fast.
The EU AI Act's August Deadline Arrives — Just Not the One Everyone Expected
GRC & Financial Crime Today Editorial Team
3 August 2026
High-risk AI obligations for financial services have been pushed back sixteen months. Transparency rules for chatbots and synthetic media have not moved at all — and enforcement power against general-purpose AI providers switches on this week.
Compliance teams that had 2 August 2026 marked as the date high-risk AI obligations would bite for financial services can stand down, at least partially. Following the European Commission's Digital Omnibus proposal and a political agreement reached in May 2026, the timetable for high-risk AI systems has shifted: stand-alone high-risk systems under Annex III — the category that includes credit-scoring engines, hiring tools and biometric systems, squarely relevant to financial institutions — now have until December 2027 rather than August 2026. AI embedded as a safety component within already-regulated products, under Annex I, has been pushed further still, to August 2028. The Commission has been careful to frame this as a resequencing to allow technical standards and supporting infrastructure to catch up, not a softening of the underlying rules.
What has not moved is more consequential in the immediate term than the headline delay suggests. Article 50 transparency obligations — the requirement to disclose to users when they are interacting with an AI chatbot, or viewing AI-generated synthetic content — remain on schedule and become enforceable from 2 August 2026. Separately, the Commission's power to enforce obligations on general-purpose AI model providers, obligations that have technically applied since August 2025, activates on the same date. Penalties for non-compliance run up to €15 million or 3% of global annual turnover, whichever is higher, putting genuine financial weight behind a set of obligations that many institutions had mentally filed under the deferred high-risk timeline.
Why This Matters More for Financial Institutions Than the Headlines Suggest
The delay applies to high-risk systems. It does not apply to the chatbot on your website, or the AI tool drafting customer-facing correspondence.
The practical risk here is a mismatch between what compliance teams have been told to prepare for and what actually takes effect this week. A bank or insurer using generative AI in customer-facing contexts — a virtual assistant handling account queries, an AI tool drafting or summarising customer correspondence, a synthetic-media disclosure in marketing content — is squarely inside Article 50's scope from 2 August 2026, irrespective of whether the underlying use case would eventually be classified as high-risk under Annex III. Institutions that treated the Digital Omnibus delay as a green light to slow down their AI governance programmes more broadly may find themselves compliant with a deadline that was deferred, while exposed on one that was not.
The Practical Response
Institutions with any customer-facing generative AI deployment should confirm, this week, that Article 50 disclosure requirements are actually implemented in production — not scheduled, not in a backlog, but live. Separately, model risk and AI governance teams should use the extended runway on Annex III obligations productively rather than as a reason to deprioritise: the technical standards the Commission is waiting on will define the actual compliance bar, and institutions that build their model inventory, documentation and human-oversight processes now will not be starting from zero when the December 2027 deadline arrives.
Sources: European Commission Digital Omnibus proposal and AI Act implementation timeline, 2026. This article is intended as general commercial awareness and does not constitute regulatory or legal advice.
Your email address will not be published. Required fields are marked with *
CPMI and IOSCO Release New Guidance on Managing Business Risks in Financial Market Infrastructures
The Committee on Payments and Market Infrastructures (CPMI) and IOSCO have released final guidance to help financial market infrastructures strengthen their approach to managing business risks and preparing for potential financial losses. The guidance clarifies existing requirements under Principle 15 of the Principles for Financial Market Infrastructures, following an assessment that identified weaknesses in how some institutions were applying the standards.
# Telemedicine CEO Sentenced to 19 Years Over $1 Billion Medicare Fraud Scheme
A Kansas healthcare technology executive has been sentenced to 19 years in prison for his role in a fraud scheme that generated more than $1 billion in claims against Medicare and other federal healthcare programmes. The case exposed how fraudulent medical orders, illegal kickbacks and deceptive telemedicine practices were used to exploit public healthcare funds.
FATF Warns Gaming and Gambling Sectors Face Growing Financial Crime Risks
The Financial Action Task Force (FATF) has identified new ways criminals are exploiting gaming and gambling platforms to move money, evade controls and support wider criminal activity. With online and cross-border gambling expanding rapidly, the FATF has issued new risk indicators to help regulators, financial institutions and industry operators detect suspicious activity and respond to money laundering, terrorist financing and other financial crime risks.
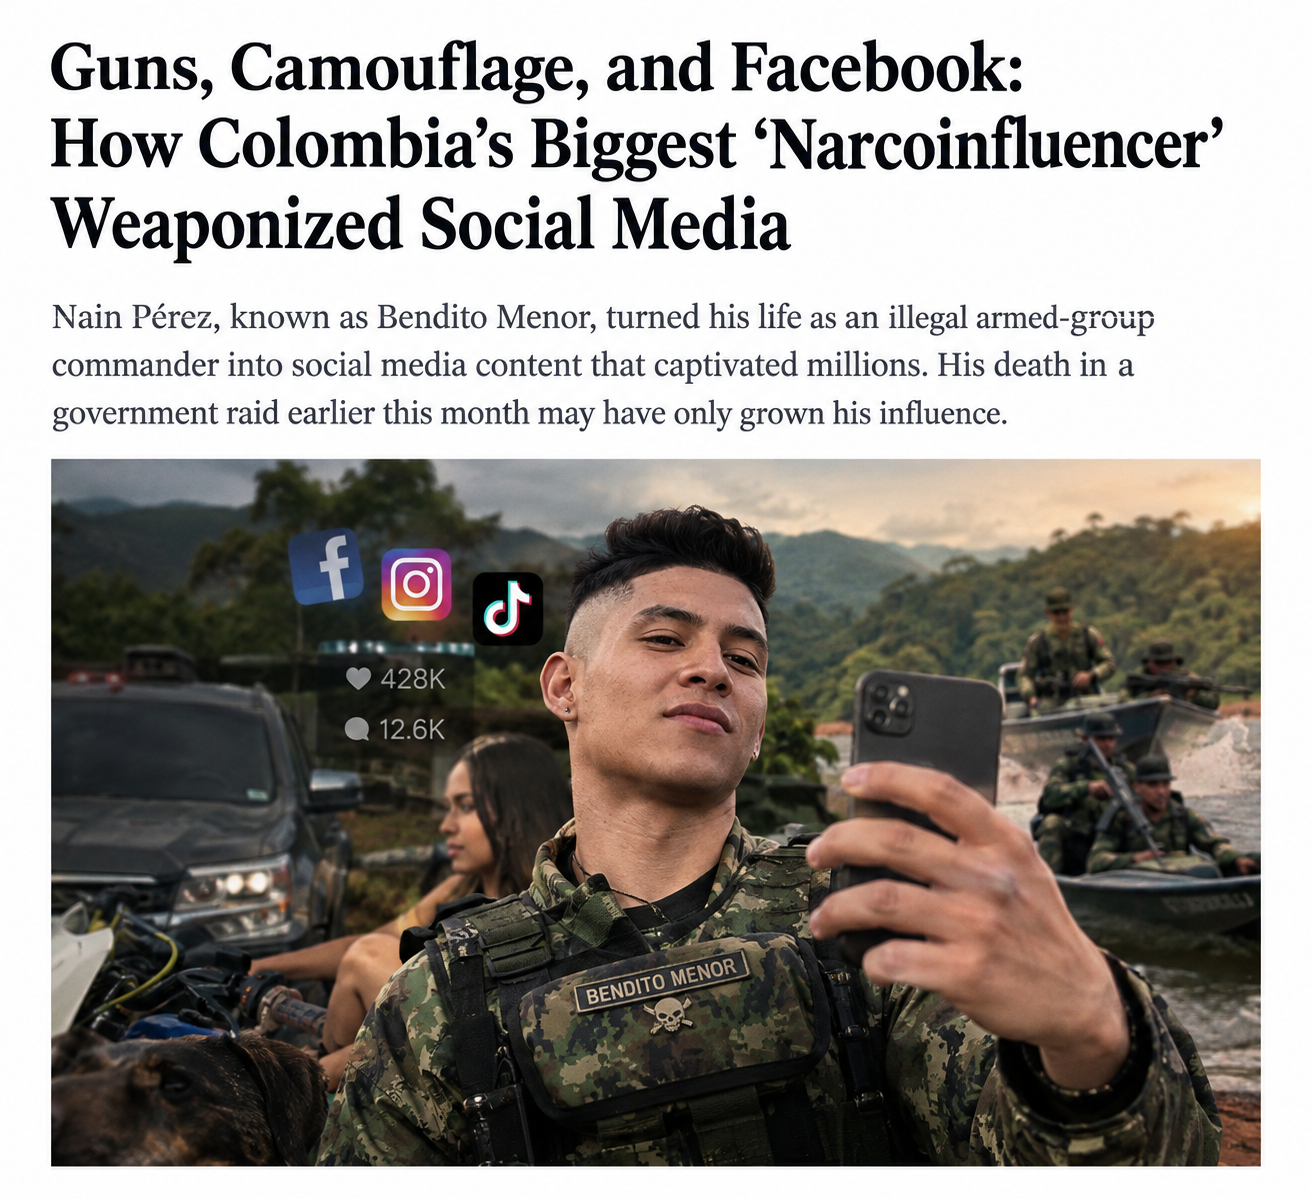
Guns, Camouflage and Facebook: How Colombia’s ‘Narcoinfluencer’ Turned Crime Into Content
Nain Pérez, known online as Bendito Menor, built a huge following by mixing images of money, romance and armed life with a criminal persona. His rise shows how social media can turn organized crime into something dangerously close to celebrity culture.
ENISA Warns Digital Dependencies Are Expanding Europe’s Cyber Attack Surface
Europe’s growing reliance on interconnected digital technologies is creating new cybersecurity challenges, with ENISA warning that increasing digital dependencies could widen the region’s exposure to cyber threats, vulnerabilities and potential disruptions across critical sectors.

A network that laundered more than four million euros from scams by sending the money to Nigeria falls
Spanish Police Bust €4 Million International Money Laundering Ring Bound for Nigeria. The Spanish Civil Guard has dismantled a criminal network responsible for laundering over €4 million generated through cyber fraud, CEO scams, and identity theft across Europe. The organization utilized "smurfing"—splitting large illicit funds into more than 9,200 small-wire transfers using falsified passports and stolen identities—to bypass anti-money laundering controls and funnel cash into Nigeria. The two-phase operation led to 20 arrests, investigations into 11 others, and raids targeting key leaders in Bilbao as well as several complicit money transfer agencies.
No recommended articles found.