
RegTech Won't Save You From a Bad Governance Model. It Will Just Automate It Faster.
Insight . Intelligence . Accountability
A new wave of professionals is transforming Governance, Risk, and Compliance from a rigid framework into a dynamic force for trust, innovation, and resilience. Governance, Risk, and Compliance (GRC) has long been associated with boardrooms and bureaucracy—a domain reserved for executives and auditors. But that image is changing fast.
RegTech Won't Save You From a Bad Governance Model. It Will Just Automate It Faster.
Dr Foluso Amusa, PhD — Founder & President, IGRCFP
3 August 2026
Every compliance leader I meet is being asked, in some form, what their AI strategy is. Almost none of them are being asked the more important question first: what is your governance model for the AI you already have?
There is a seductive logic to RegTech procurement that goes roughly as follows: our transaction monitoring generates too many false positives, or our KYC process is too slow, or our sanctions screening misses context a human would catch — therefore we need an AI-powered tool to fix it. The logic is not wrong, exactly. It is incomplete. A tool that automates a poorly governed process does not fix the process. It removes the friction that was, however inefficiently, forcing a human to notice when something looked wrong.
I have watched this play out inside institutions that were, on paper, sophisticated adopters of financial crime technology. A machine-learning transaction monitoring model was deployed to replace a rules-based system that generated too much noise. Alert volumes dropped, analyst productivity metrics improved, and the project was declared a success in the quarterly steering committee. Eighteen months later, a regulator asked a simple question during an examination: can you explain, in terms a customer could understand, why this specific transaction was or was not flagged? The institution could not answer with any confidence, because nobody had built the explainability and model validation layer that would have made the answer possible. The tool worked. The governance around the tool did not exist yet.
Explainability Is Not Optional, and It Is Not the Vendor's Job
If your model risk framework cannot explain a decision, you don't have an AI capability. You have a black box with a service level agreement.
This is the uncomfortable part of AI adoption in financial crime and compliance functions: the accountability for a model's output sits with the institution deploying it, not with the vendor who built it, and regulators globally are converging on that position regardless of how the underlying technology is licensed. A model inventory that does not include third-party and embedded AI tools is incomplete. A validation process that treats a vendor's own testing as sufficient evidence of soundness is inadequate. And a governance committee that cannot articulate, in plain language, how a high-stakes model reaches its conclusions has not actually solved the problem it set out to solve — it has simply moved the point of failure from a human analyst to a system nobody in the room can fully interrogate.
A Simple Test Before You Deploy
Institutions considering AI or RegTech adoption in financial crime, KYC or compliance functions would do well to apply a simple test before signing a contract: could you explain this tool's decision-making to a regulator, in an examination, without the vendor in the room? If the honest answer is no, the gap is not technological. It is governance — the same discipline of clear accountability, documented process and board-level oversight that has always separated institutions that manage risk well from institutions that simply generate the paperwork suggesting they do. Technology changes the speed and scale of that discipline. It does not change the discipline itself.
This article reflects the author's professional view and is intended for general awareness. It does not constitute regulatory or legal advice.
Your email address will not be published. Required fields are marked with *
CPMI and IOSCO Release New Guidance on Managing Business Risks in Financial Market Infrastructures
The Committee on Payments and Market Infrastructures (CPMI) and IOSCO have released final guidance to help financial market infrastructures strengthen their approach to managing business risks and preparing for potential financial losses. The guidance clarifies existing requirements under Principle 15 of the Principles for Financial Market Infrastructures, following an assessment that identified weaknesses in how some institutions were applying the standards.
# Telemedicine CEO Sentenced to 19 Years Over $1 Billion Medicare Fraud Scheme
A Kansas healthcare technology executive has been sentenced to 19 years in prison for his role in a fraud scheme that generated more than $1 billion in claims against Medicare and other federal healthcare programmes. The case exposed how fraudulent medical orders, illegal kickbacks and deceptive telemedicine practices were used to exploit public healthcare funds.
FATF Warns Gaming and Gambling Sectors Face Growing Financial Crime Risks
The Financial Action Task Force (FATF) has identified new ways criminals are exploiting gaming and gambling platforms to move money, evade controls and support wider criminal activity. With online and cross-border gambling expanding rapidly, the FATF has issued new risk indicators to help regulators, financial institutions and industry operators detect suspicious activity and respond to money laundering, terrorist financing and other financial crime risks.
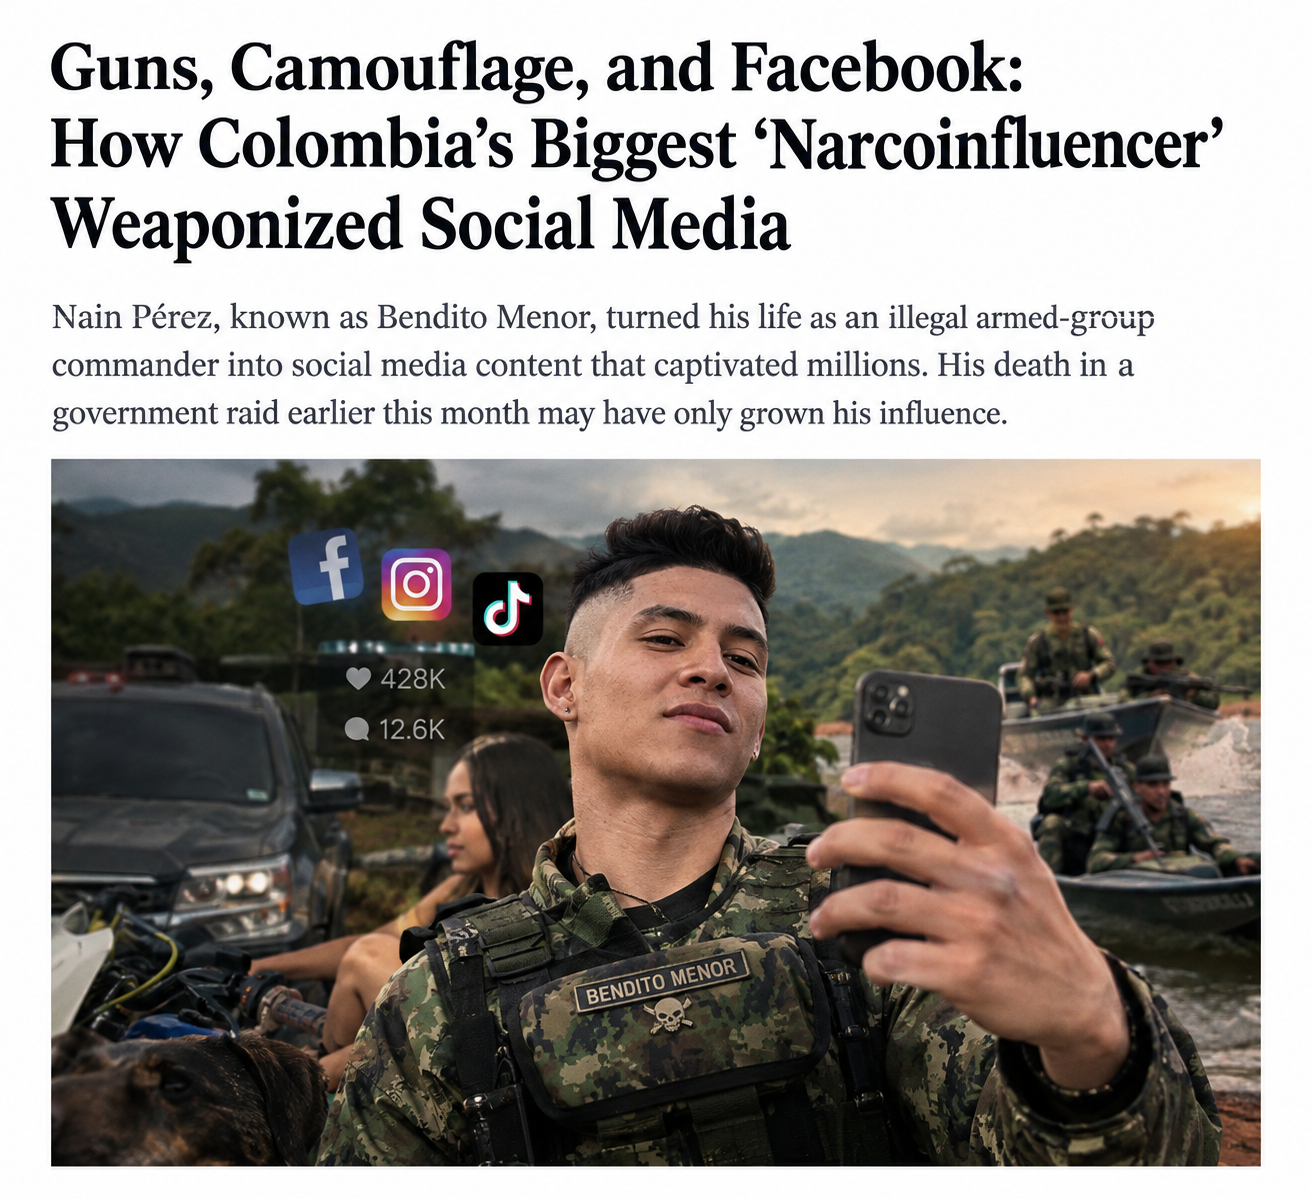
Guns, Camouflage and Facebook: How Colombia’s ‘Narcoinfluencer’ Turned Crime Into Content
Nain Pérez, known online as Bendito Menor, built a huge following by mixing images of money, romance and armed life with a criminal persona. His rise shows how social media can turn organized crime into something dangerously close to celebrity culture.
ENISA Warns Digital Dependencies Are Expanding Europe’s Cyber Attack Surface
Europe’s growing reliance on interconnected digital technologies is creating new cybersecurity challenges, with ENISA warning that increasing digital dependencies could widen the region’s exposure to cyber threats, vulnerabilities and potential disruptions across critical sectors.

A network that laundered more than four million euros from scams by sending the money to Nigeria falls
Spanish Police Bust €4 Million International Money Laundering Ring Bound for Nigeria. The Spanish Civil Guard has dismantled a criminal network responsible for laundering over €4 million generated through cyber fraud, CEO scams, and identity theft across Europe. The organization utilized "smurfing"—splitting large illicit funds into more than 9,200 small-wire transfers using falsified passports and stolen identities—to bypass anti-money laundering controls and funnel cash into Nigeria. The two-phase operation led to 20 arrests, investigations into 11 others, and raids targeting key leaders in Bilbao as well as several complicit money transfer agencies.
No recommended articles found.